Passwords alone don’t cut it anymore. Setting up multi-factor authentication in Microsoft 365 is one of the simplest, highest-impact security changes a small business can make – Microsoft’s own research shows MFA blocks 99.22% of account compromise attempts. If you haven’t switched it on yet, here’s the good news: it takes less time than you’d think, and this guide walks through exactly how to do it.
What Is Multi-Factor Authentication (and Why It Matters)
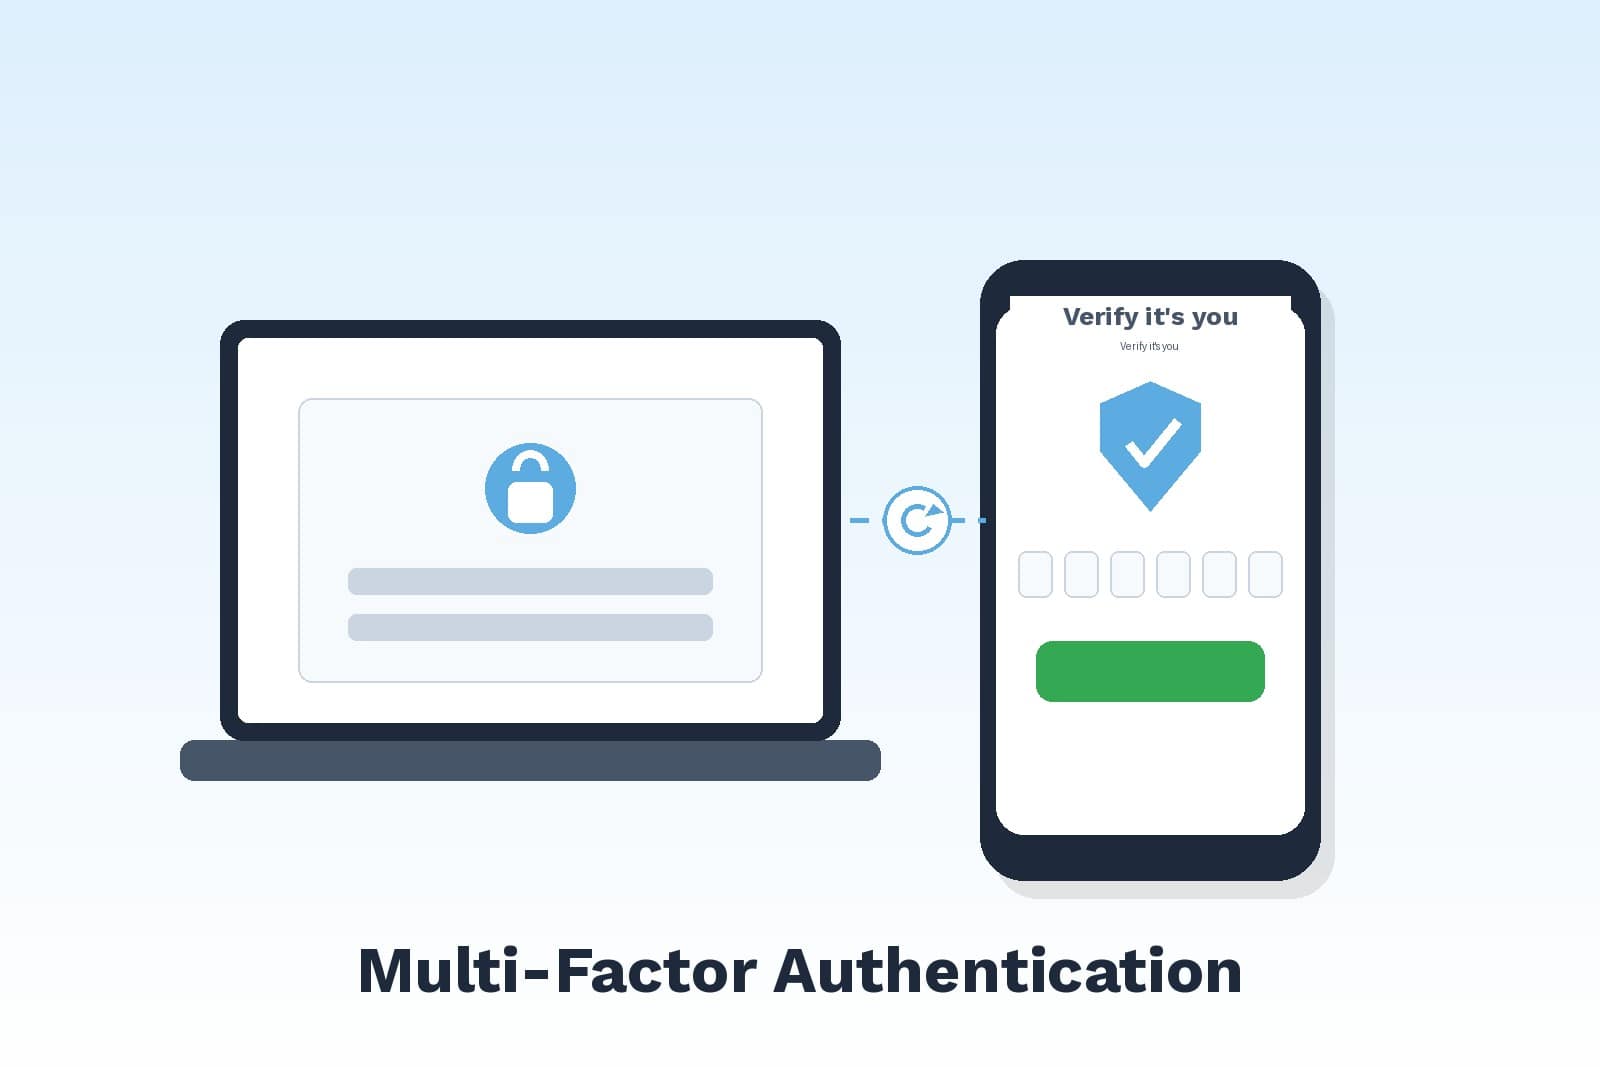
MFA simply means proving who you are with more than just a password. After entering your password, you confirm your identity a second way – typically a code from an app on your phone, a push notification you approve, or a fingerprint. Even if a criminal steals or guesses your password, they’re stopped at that second step.
It matters more than ever because Microsoft itself now treats MFA as essential rather than optional: since February 2025, Microsoft has been rolling out mandatory MFA for anyone accessing the Microsoft 365 admin center, phased in tenant by tenant. If your business hasn’t set it up yet, you’ll be required to soon regardless – so it’s worth doing properly now, on your own terms.
Before You Start: What You’ll Need
- Admin access – you’ll need Global Administrator or Security Administrator rights in Microsoft 365 to change these settings.
- Your licence type – check under Billing > Licenses in the admin center. Business Basic and Standard plans include Microsoft Entra ID Free, which covers Security Defaults. Business Premium includes Entra ID P1, which unlocks Conditional Access policies for more control.
- A plan for your team – give staff at least a week’s notice before switching MFA on, so nobody’s caught off guard mid-task.
Step-by-Step: Setting Up Multi-Factor Authentication in Microsoft 365
There are two main routes, depending on your licence and how much control you want.
Option 1: Security Defaults (the Fastest, Free Option)
Security Defaults give every user a baseline level of MFA protection with no configuration required, and they’re included free with every Microsoft 365 plan. In fact, if your tenant was created after October 2019, there’s a good chance they’re already switched on.
- Sign in to the Microsoft Entra admin center with a Global Administrator or Security Administrator account.
- Go to Identity > Overview.
- Select the Properties tab.
- Scroll to Security defaults and select Manage security defaults.
- Toggle security defaults to Enabled and save.
This is the right choice if you want strong protection today with zero ongoing management. The trade-off is flexibility: it’s all-or-nothing across your whole organisation, with no ability to fine-tune by role, location, or app.
Option 2: Conditional Access Policies (More Control, Needs Business Premium)
Conditional Access lets you set smarter rules – for example, requiring MFA only when someone signs in from an unrecognised location or device, while trusting your usual office network. It needs Entra ID P1, included in Business Premium.
- In the Microsoft Entra admin center, go to Protection > Conditional Access > Policies.
- Select New policy.
- Give it a clear name, e.g. “Require MFA for all users”.
- Under Assignments > Users, include all users – but exclude your emergency access account (see the mistake to avoid below).
- Under Target resources, select All resources.
- Under Grant, choose Grant access and tick Require multifactor authentication.
- Set the policy to Report-only first, review the sign-in logs for a few days, then switch it to On once you’re confident it won’t lock anyone out unexpectedly.
Getting Your Team Set Up
Once MFA is switched on, each user will be prompted to register a verification method next time they sign in (or you can send them directly to aka.ms/mfasetup). Point your team toward the Microsoft Authenticator app as their primary method rather than SMS text codes – it’s free, faster to use, and meaningfully more secure since SMS can be intercepted.
Common Mistakes to Avoid
- No break-glass account. Always keep at least one emergency admin account excluded from your MFA/Conditional Access policies, with a long, securely stored password. If your Conditional Access policy misfires, this is what stops you being locked out of your own tenant.
- Rolling out to everyone at once. Test with a small group first, ideally including someone in IT and one non-technical user, before switching it on organisation-wide.
- Relying only on SMS. It works, but app-based push notifications and authenticator codes are harder to intercept and more reliable.
- Running legacy per-user MFA alongside Conditional Access. These two systems can conflict. If you’re moving to Conditional Access, turn off the old per-user MFA settings under Users > Active users first.
Get It Set Up Right, First Time
Getting multi-factor authentication in Microsoft 365 configured correctly is one of the highest-value, lowest-cost security changes any small business can make – but a rushed rollout can cause real disruption if break-glass accounts, licensing, or policy scope aren’t planned properly. We help clients configure Microsoft 365 security correctly the first time, as part of our wider cybersecurity and data protection support.
Get in touch if you’d like a hand rolling this out across your business without the risk of locking your own team out.